Attackers frequently target less-secure vendors as a backdoor to breach their primary targets, making your partners a significant risk vector. Effective vendor risk management identifies and mitigates vulnerabilities within your supply chain before they can impact your business operations. Protecting your perimeter is no longer enough; you must also ensure the security of everyone you do business with.

Third-Party & Supply Chain Risk Management
Your security posture is only as strong as your weakest vendor. We assess supplier ecosystems, validate controls through questionnaires and evidence, and establish continuous monitoring for critical dependencies.

Scope of Assessment
What We Assess
The areas we examine during a Third-Party & Supply Chain Risk Management engagement, and what each one is looking for.
01
Vendor Risk Profiling
Define risk profiling and tiering criteria based on vendor business criticality and data access.
02
Questionnaire Auditing
Audit third-party security questionnaires, self-assessments, and supporting evidence.
03
Continuous Monitoring
Configure continuous exposure monitoring for critical supplier networks and domains.
04
Contract Review
Review service level agreements (SLAs) and contractual cybersecurity requirements for vendors.
05
N-th Party Mapping
Map downstream N-th party vendor dependencies to find hidden ecosystem risks.
Also in Scope
Third-party incident response coordination and breach notification obligations
Vendor security posture changes and trigger-based reassessment protocols
Open-source and software component risk within the supply chain
Regulatory and compliance obligations tied to third-party data handling
Offboarding and access revocation controls for departing vendors and partners
Concentration risk across critical third-party service dependencies
Engagement Sequence
How QuassrCyberTech Delivers
A structured delivery sequence that converts assessment insights into measurable resilience outcomes.
01
Scope & Discovery
Build third-party inventory, criticality mapping, and business dependency context.
02
Evaluate & Gap Map
Assess vendor controls, identify concentration risk, and map framework gaps.
03
Craft Strategy
Define risk treatment and governance actions aligned to business impact.
04
Upskill & Implement
Operationalize workflows, reporting templates, and ownership model.
05
Review & Evolve
Run periodic reassessment cycles and update controls for changing supplier risk.
Where This Lands
Industry Application
Enterprise & Manufacturing
Managing third-party cyber risk across complex, global supplier ecosystems and operational dependencies.
Banking & Financial Services
Ensuring outsourced technology partners align with strict financial regulatory security requirements.
Powered by the QuassrCyberTech ecosystem
Platform intelligence that accelerates delivery, strengthens execution, and improves measurable outcomes.

AI-Powered Asset Intelligence & Vulnerability Management
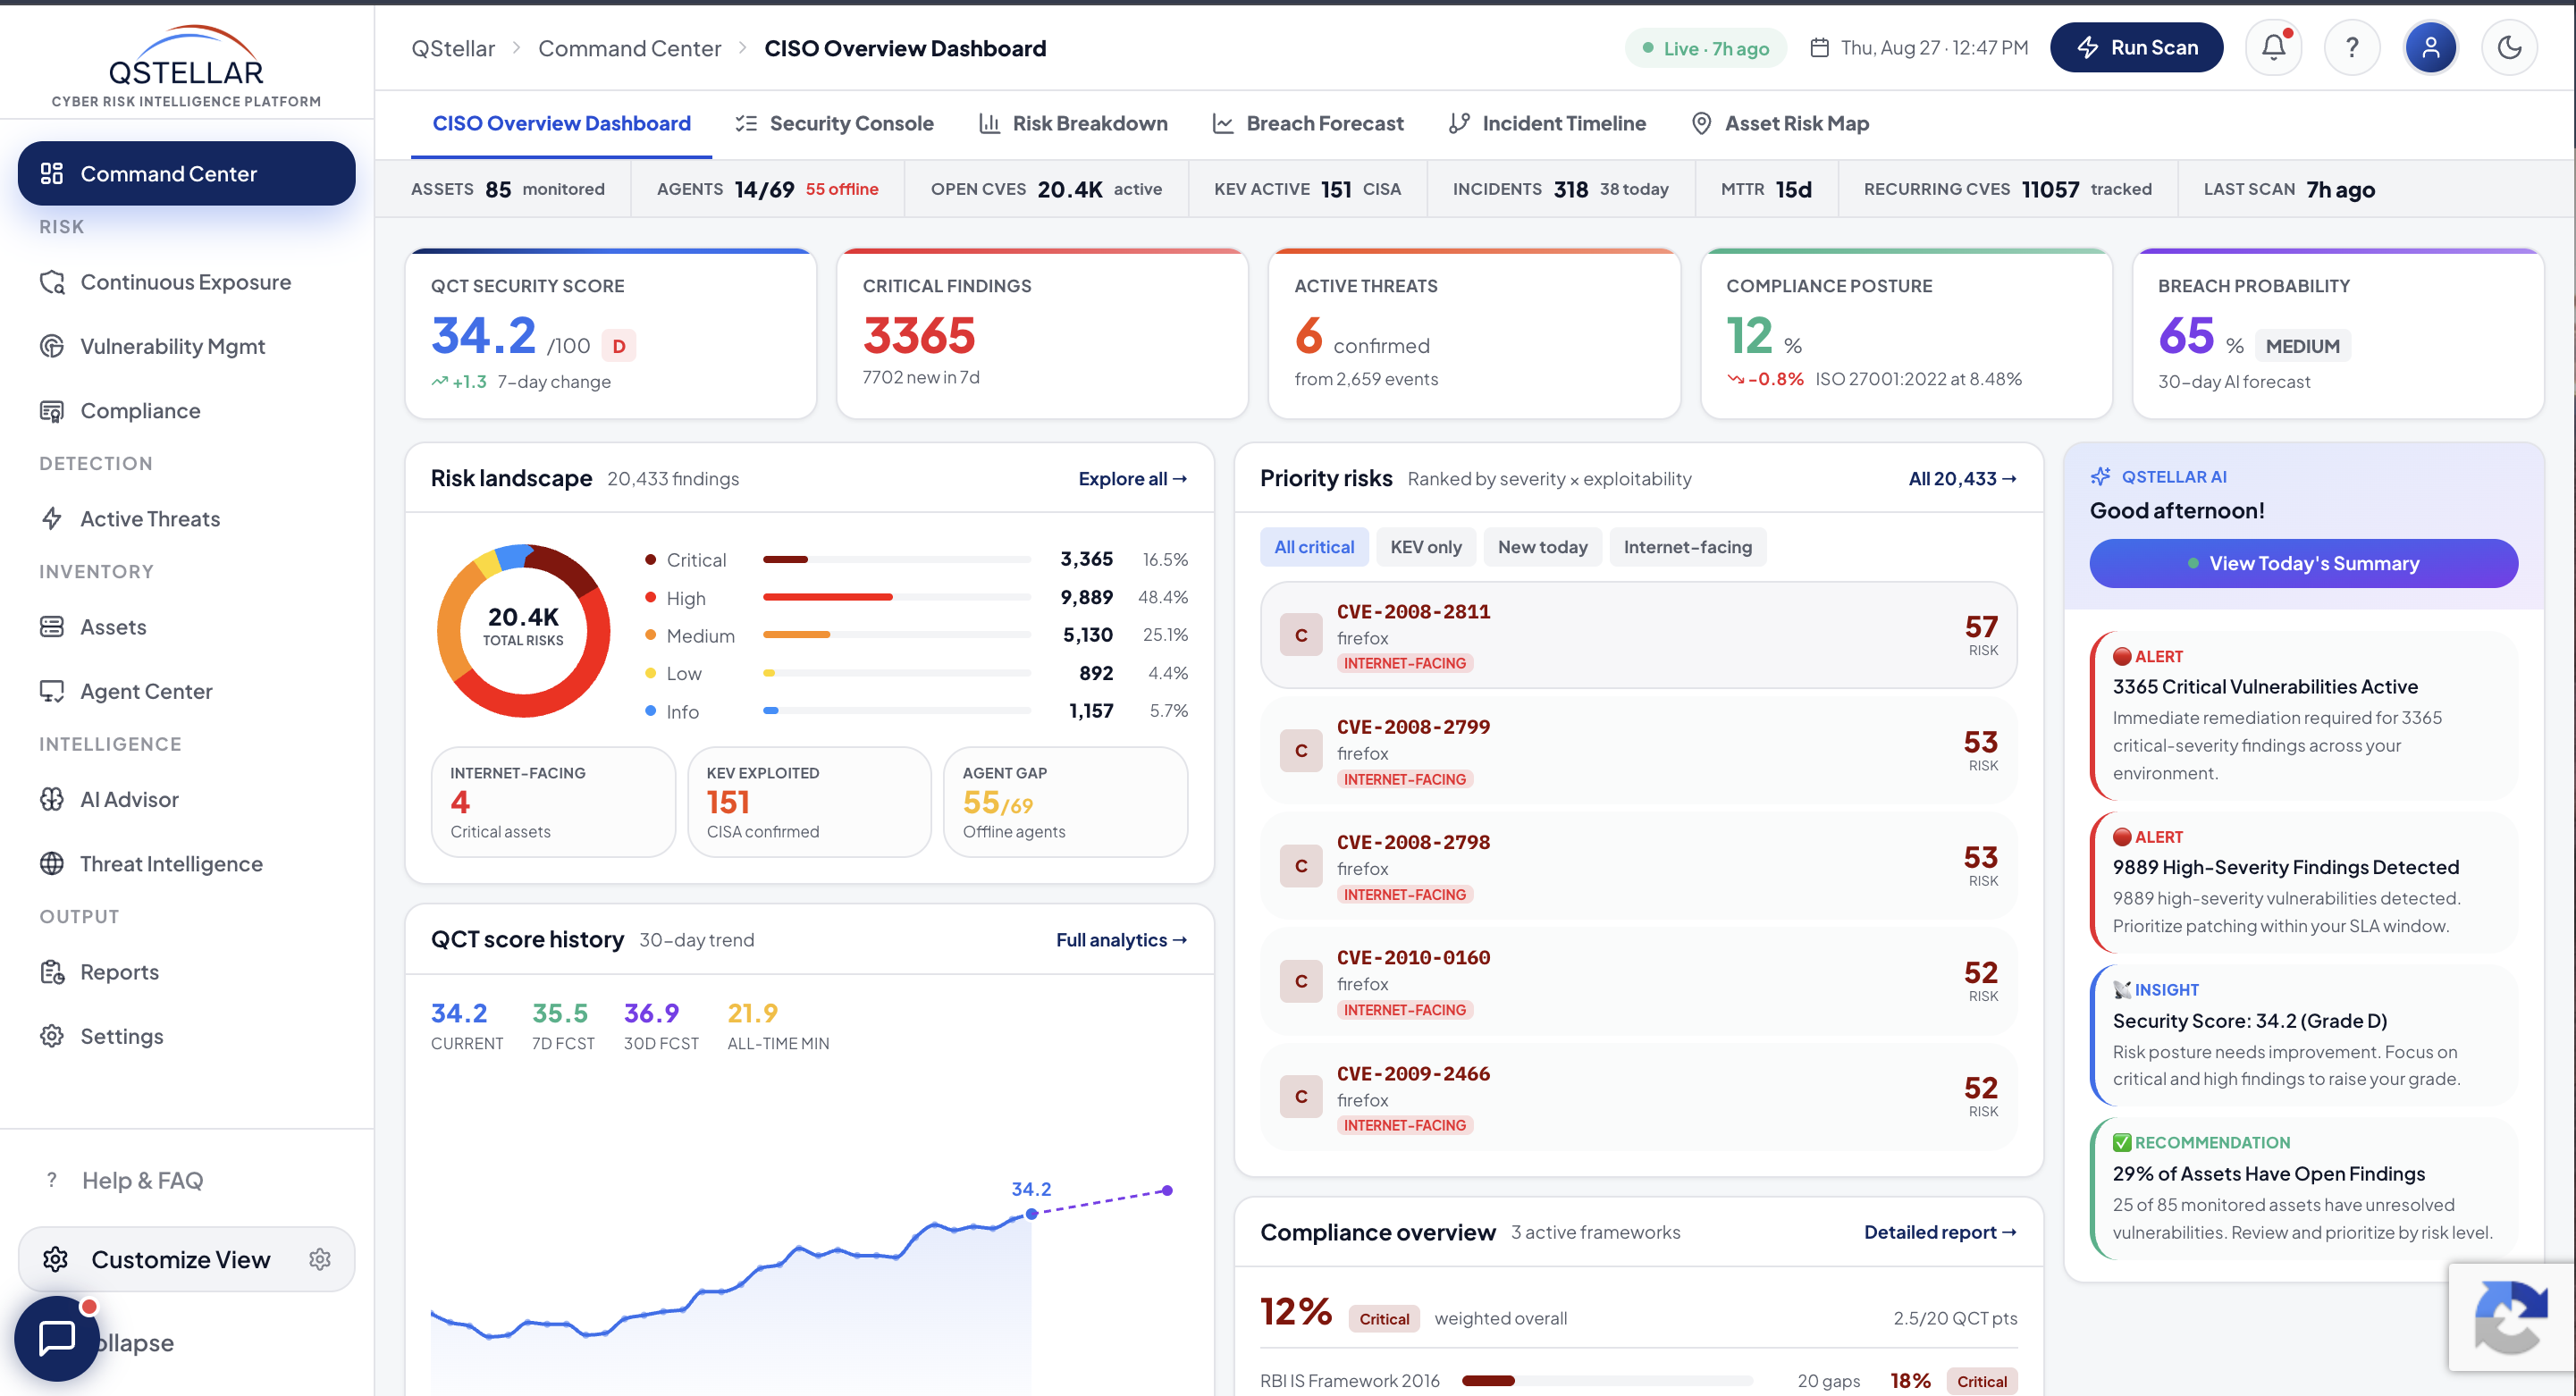
Our Third-Party & Supply Chain Risk Management engagements are accelerated by QStellar, combining platform intelligence with advisory and execution delivery.
- Asset discovery and continuous visibility
- Vulnerability intelligence with risk prioritization
- Configuration drift and exposure monitoring
Frequently Asked Questions
Answers to common questions for Third-Party & Supply Chain Risk Management.
Related Capabilities
Explore adjacent capability pillars commonly delivered alongside this engagement stream.
READY TO BEGIN?
Secure Your Digital Enterprise
Partner with QuassrCyberTech to strengthen cyber resilience, governance, and security operations.