We translate complex technical threats into clear business impacts, helping leadership understand board cyber risk in a language they recognize. By quantifying potential financial and operational losses, we enable informed decision-making that protects the organization's critical assets and market reputation. Our goal is to ensure that cyber risk is integrated into the broader enterprise risk management strategy.

Executive Cyber Security Advisory
Executive Cyber Security Advisory helps leadership teams convert cyber uncertainty into a clear decision agenda. We align business priorities, threat exposure, and governance accountability so strategic programs move faster with controlled risk.

Scope of Assessment
What We Assess
The areas we examine during a Executive Cyber Security Advisory engagement, and what each one is looking for.
01
Board Risk Visibility
Assess board and executive cyber risk visibility and reporting maturity across business units.
02
Investment Alignment
Align cybersecurity investments with strategic business growth objectives and risk appetite.
03
Governance Clarity
Evaluate governance operating model clarity across executive leadership and control functions.
04
Decision Readiness
Measure decision readiness for high-impact cyber incidents and increasing regulatory pressure.
05
Ecosystem Exposure
Map and analyze third-party and supply chain risk exposure affecting key business commitments.
Also in Scope
Regulatory landscape shifts and jurisdictional obligations influencing executive cyber strategy
Cyber risk quantification models used for board-level financial impact reporting
Security leadership accountability structures and escalation pathways
Emerging threat intelligence alignment with executive risk tolerance
Business continuity dependencies and their cyber risk exposure at the leadership level
Crisis communication readiness for cyber incidents affecting organizational reputation
Engagement Sequence
How QuassrCyberTech Delivers
A structured delivery sequence that converts assessment insights into measurable resilience outcomes.
01
Discovery
Stakeholder interviews and rapid current-state baseline assessment.
02
Risk Mapping
Identify and prioritize key risk areas affecting strategic commitments.
03
Framework Alignment
Map to NIST, ISO 27001, or custom enterprise frameworks.
04
Roadmap Delivery
Provide an actionable 12-month security improvement plan.
Where This Lands
Industry Application
Banking & Financial Services
Securing core banking systems, digital payment gateways, and regulatory compliance for global financial institutions.
Enterprise & Manufacturing
Aligning cybersecurity strategy with operational resilience and large-scale industrial asset protection.

Healthcare & HealthTech
Designing strategic trust boundaries for systems handling sensitive patient data and health records.
Powered by the QuassrCyberTech ecosystem
Platform intelligence that accelerates delivery, strengthens execution, and improves measurable outcomes.

AI-Powered Asset Intelligence & Vulnerability Management
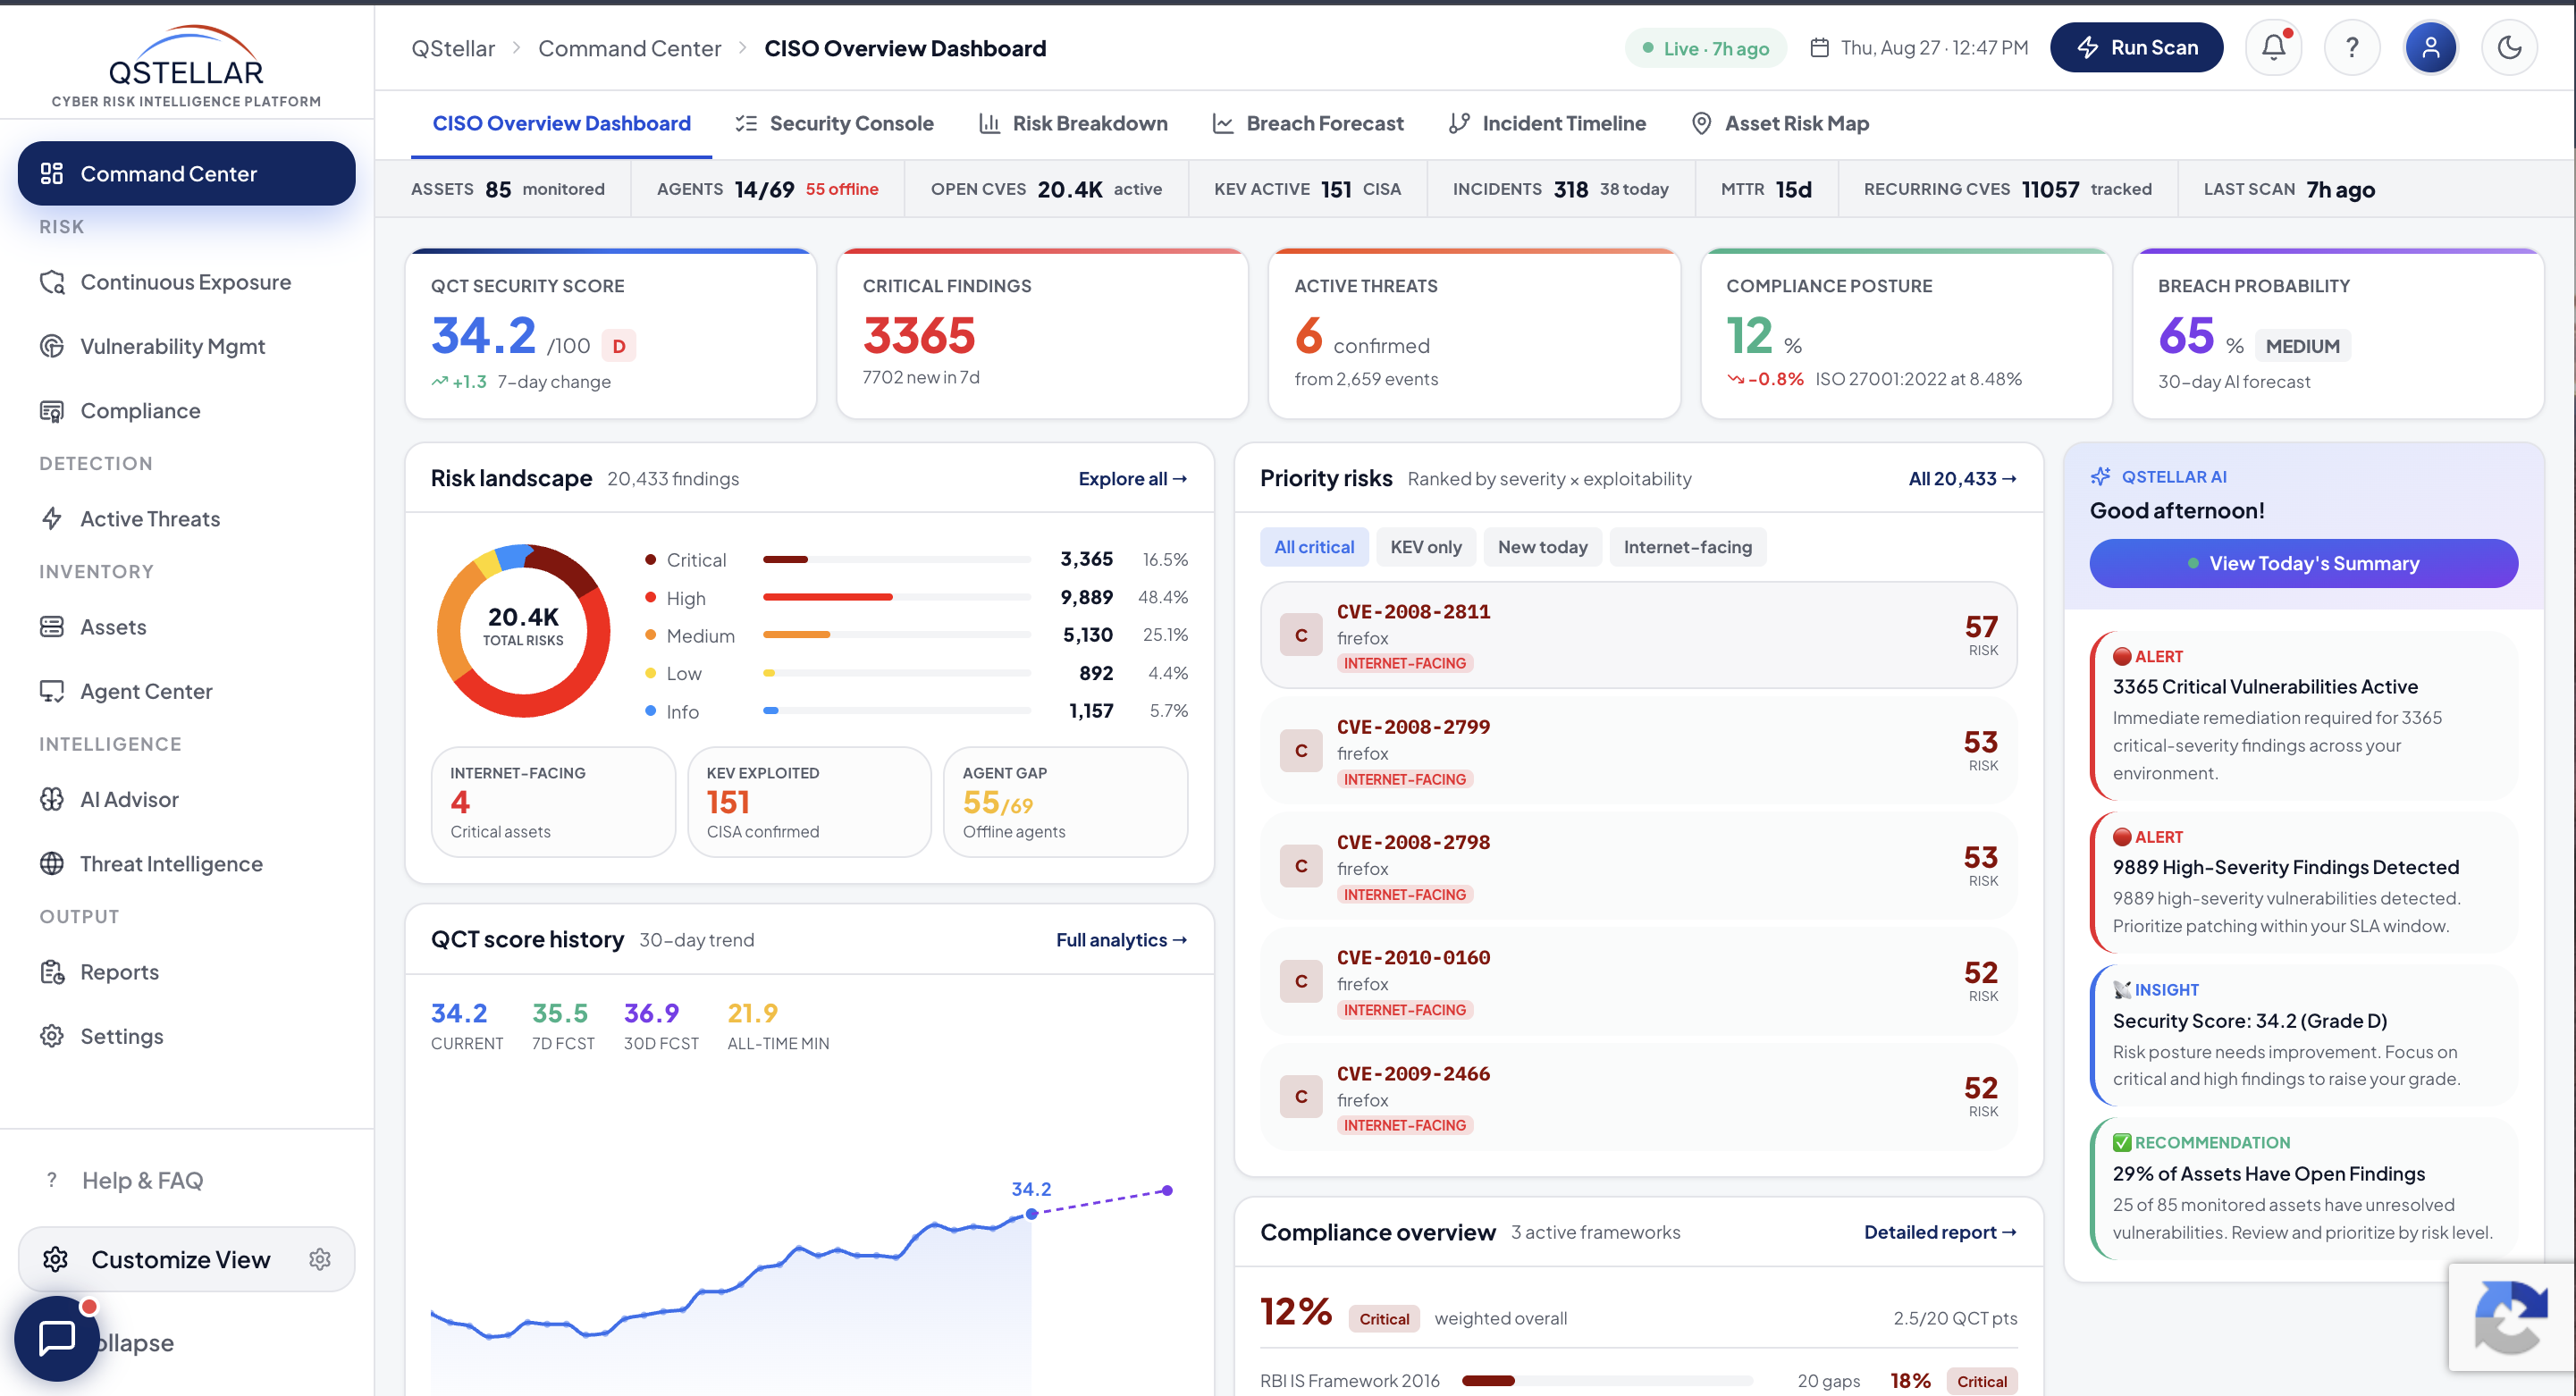
Our Executive Cyber Security Advisory engagements are accelerated by QStellar, combining platform intelligence with advisory and execution delivery.
- Asset discovery and continuous visibility
- Vulnerability intelligence with risk prioritization
- Configuration drift and exposure monitoring
Frequently Asked Questions
Answers to common questions for Executive Cyber Security Advisory.
Related Capabilities
Explore adjacent capability pillars commonly delivered alongside this engagement stream.
READY TO BEGIN?
Secure Your Digital Enterprise
Partner with QuassrCyberTech to strengthen cyber resilience, governance, and security operations.