We draft customized, actionable security policies covering critical areas like acceptable use, data protection, and granular access control. These policies form the governing rules that dictate your organization's security posture and cultural expectations. By aligning these policies with your business operations, we ensure they are both effective and easy for employees to follow.

Security Program Development
A security program is more than tools - it is people, process, and technology working together. We design programs that scale with your business.

Scope of Assessment
What We Assess
The areas we examine during a Security Program Development engagement, and what each one is looking for.
01
Policy & Frameworks
Review existing cybersecurity policies, operational procedures, and governance documentation.
02
Team Capability Gaps
Analyze security team organizational structure and identify technical capability or skill gaps.
03
Tooling Coverage
Inspect the cybersecurity technology stack to identify overlap, gaps, and integration limits.
04
Historical Incidents
Investigate previous incident records to discover recurring vulnerabilities and risk patterns.
05
Regulatory Alignment
Align security program goals with legal, contract, and compliance obligations.
Also in Scope
Risk appetite definition and security control prioritization methodology
Security awareness and training programme design and behavioral effectiveness
Third-party and vendor security integration requirements within the programme
Metrics, dashboards and reporting frameworks tracking programme performance
Business continuity and resilience alignment across programme objectives
Security ownership and accountability mapping across business functions
Programme gap analysis against industry frameworks such as NIST, ISO 27001 or CIS
Threat modeling integration into programme design and control selection
Change management and communication strategy for security programme rollout
Programme review cadence and continuous improvement governance mechanisms
Engagement Sequence
How QuassrCyberTech Delivers
A structured delivery sequence that converts assessment insights into measurable resilience outcomes.
01
Assessment
Baseline your current security program maturity against industry standards.
02
Design
Build a structured program framework across people, processes, and technology.
03
Implementation
Assist with policy creation, tool selection, and security team training.
04
Measurement
Establish KPIs, executive dashboards, and continuous improvement loops.
Where This Lands
Industry Application
Enterprise & Manufacturing
Standardizing fragmented security practices across global operational units.

SaaS & Technology
Accelerating enterprise procurement cycles by implementing scalable, audit-ready security programs.
Banking & Financial Services
Maturing internal security controls to exceed baseline regulatory expectations.
Powered by the QuassrCyberTech ecosystem
Platform intelligence that accelerates delivery, strengthens execution, and improves measurable outcomes.

AI-Powered Asset Intelligence & Vulnerability Management
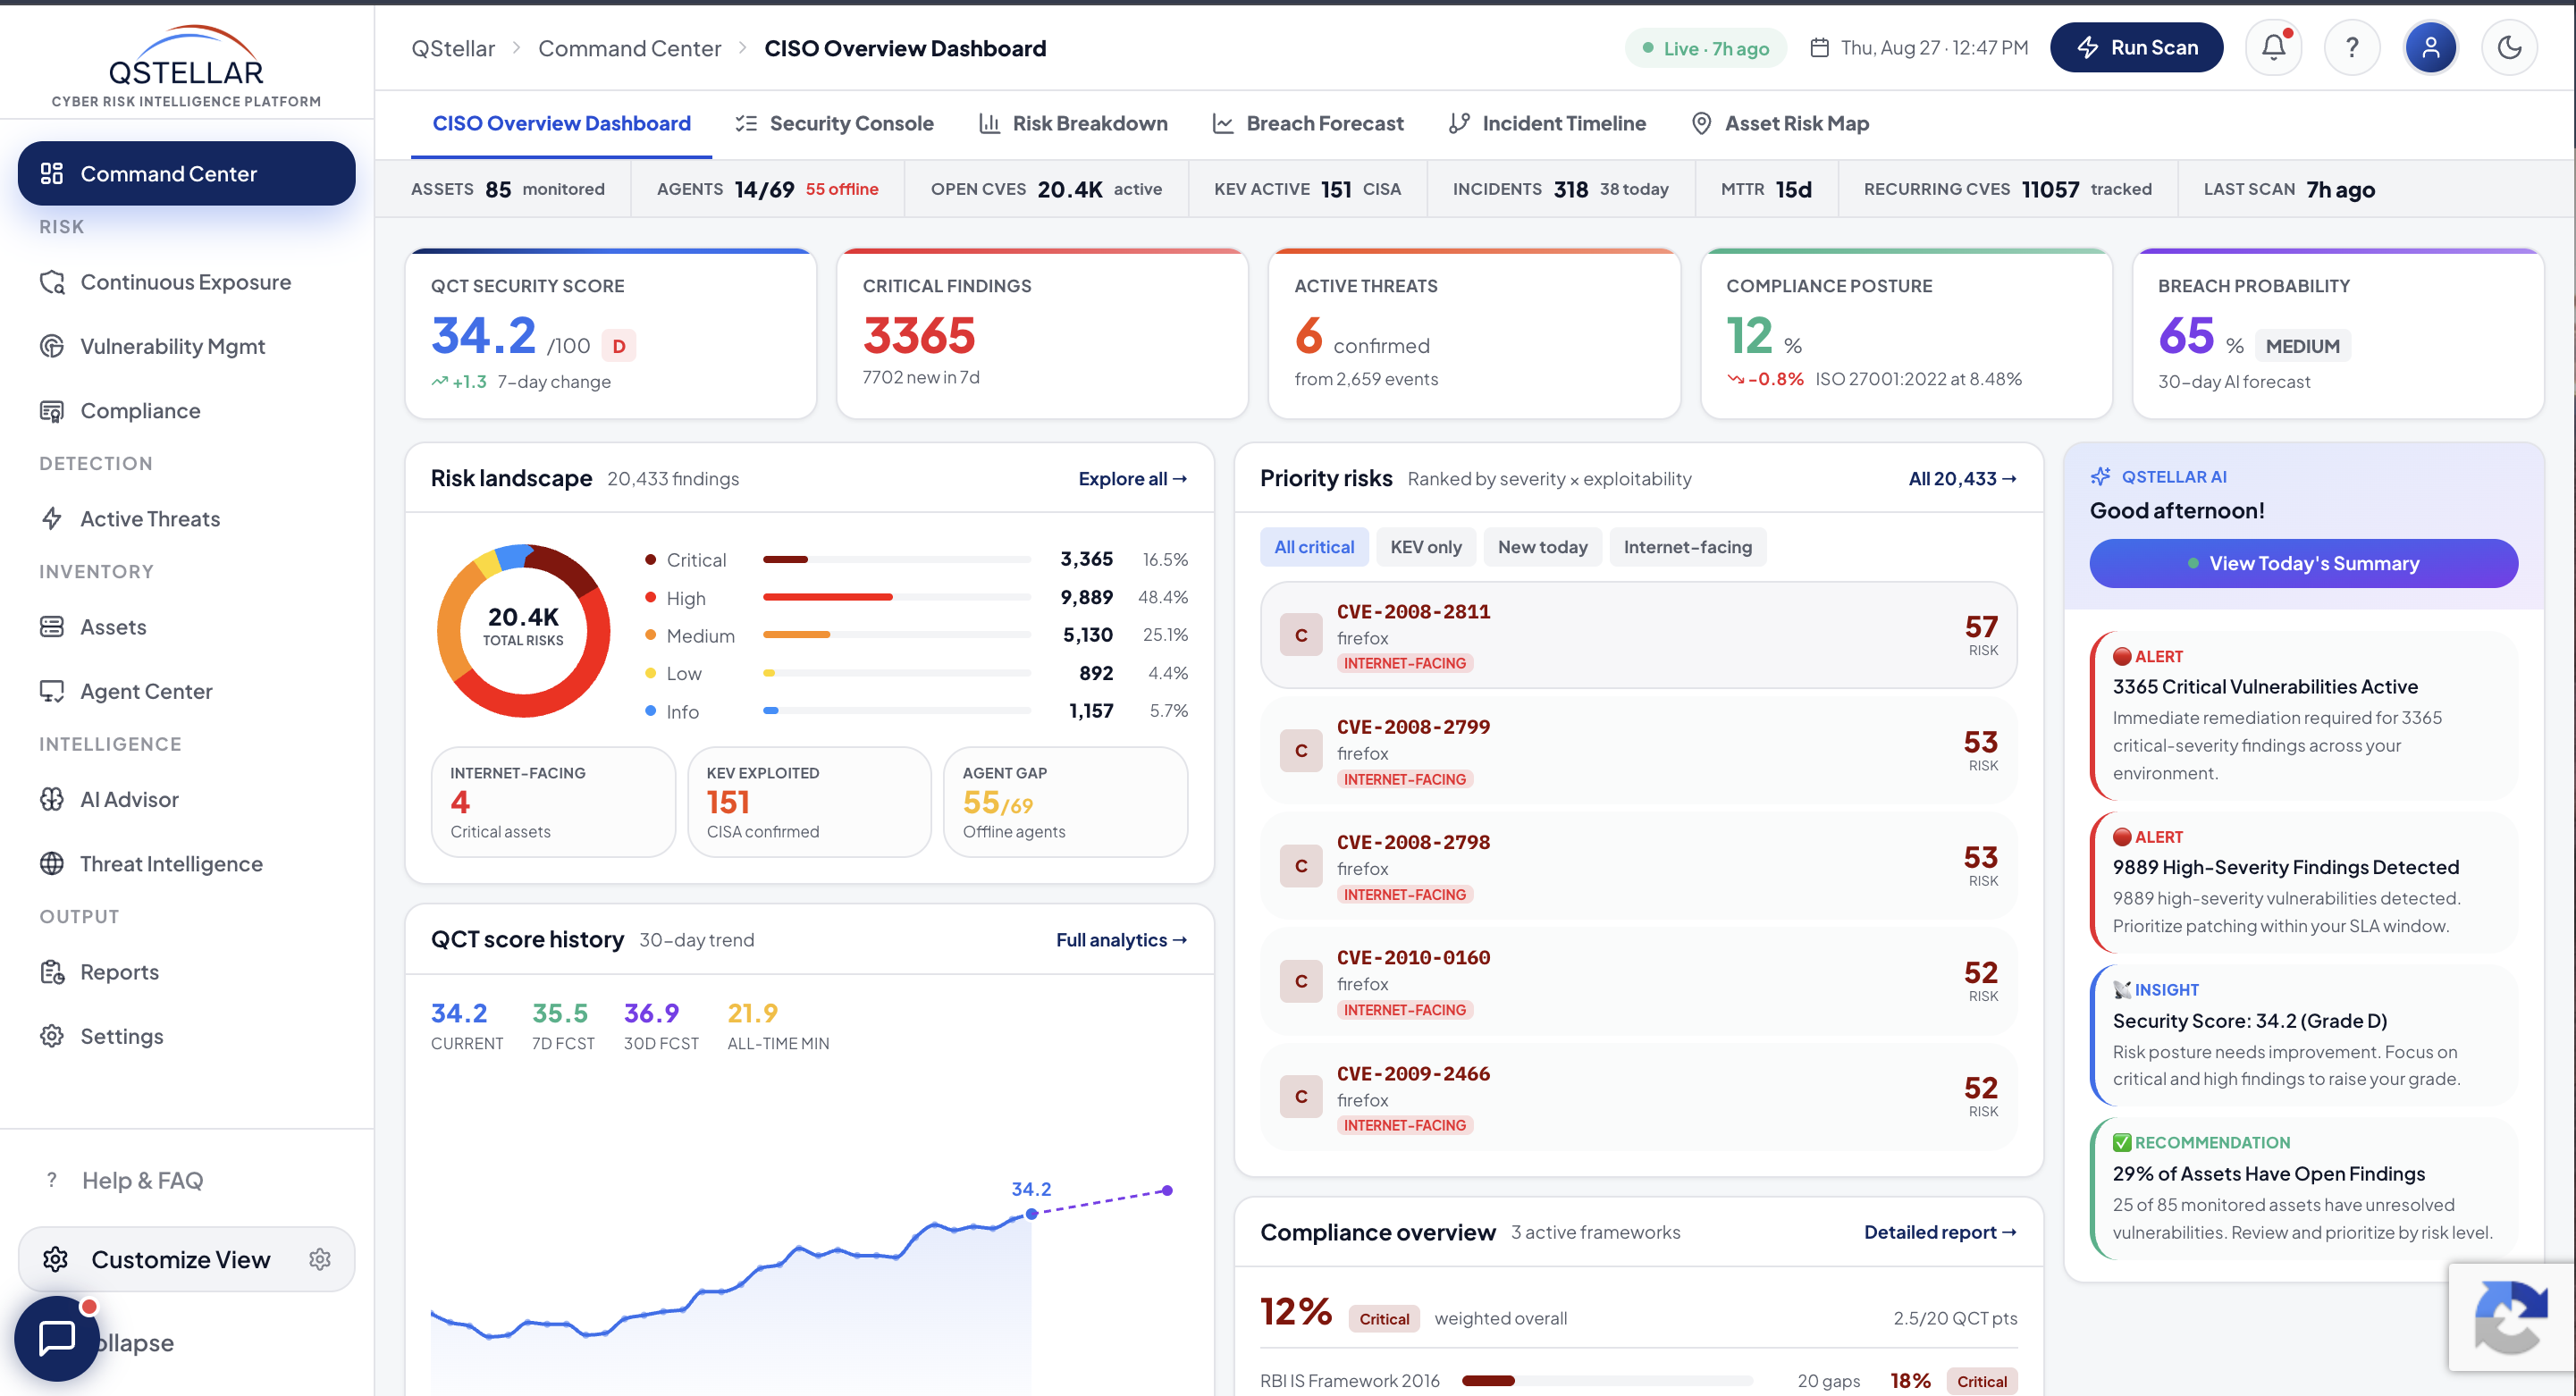
Our Security Program Development engagements are accelerated by QStellar, combining platform intelligence with advisory and execution delivery.
- Asset discovery and continuous visibility
- Vulnerability intelligence with risk prioritization
- Configuration drift and exposure monitoring
Frequently Asked Questions
Answers to common questions for Security Program Development.
Related Capabilities
Explore adjacent capability pillars commonly delivered alongside this engagement stream.
READY TO BEGIN?
Secure Your Digital Enterprise
Partner with QuassrCyberTech to strengthen cyber resilience, governance, and security operations.