SOC2 is a widely recognized auditing standard that proves your organization securely manages and protects client data. Clients demand it as verifiable proof that you have strong, audited security practices in place before they trust you with their data. Achieving SOC2 compliance is often a prerequisite for winning major enterprise contracts and expanding into global markets.

SOC2 Readiness
SOC2 certification is increasingly a prerequisite for enterprise sales. We get you audit-ready efficiently - without disrupting your engineering team.

Scope of Assessment
What We Assess
The areas we examine during a SOC2 Readiness engagement, and what each one is looking for.
01
Trust Criteria Coverage
Scope and map operational controls to all relevant SOC 2 Trust Service Criteria.
02
SOC 2 Gap Analysis
Review current operational controls against SOC 2 security framework requirements.
03
Evidence Workflows
Assess and automate evidence collection workflows and supporting audit tools.
04
Subprocessor Management
Audit compliance agreements, security reports, and risk profiles of subprocessors.
05
Operational Lifecycle
Review software change management controls, deployment logs, and incident responses.
Also in Scope
Logical access provisioning, review and deprovisioning controls
Encryption and data protection controls across storage and transmission
Vulnerability management and penetration testing programme adequacy
Business continuity and disaster recovery plan documentation and testing
Employee background verification and security awareness training processes
Network monitoring, intrusion detection and alerting control coverage
Data retention, disposal and media sanitization control alignment
Risk assessment process documentation and periodic review cadence
System description accuracy and boundary definition for audit scope
Audit readiness timeline, resource allocation and auditor engagement planning
Engagement Sequence
How QuassrCyberTech Delivers
A structured delivery sequence that converts assessment insights into measurable resilience outcomes.
01
Scoping
Define applicable Trust Service Criteria and organizational system boundaries.
02
Readiness Assessment
Perform a detailed gap analysis against the chosen SOC2 criteria.
03
Remediation
Implement missing controls in collaboration with your engineering team.
04
Auditor Support
Build the evidence package and manage auditor queries during fieldwork.
Where This Lands
Industry Application

SaaS & Technology
Achieving rapid SOC2 Type II compliance to unlock tier-1 enterprise sales.
FinTech & Digital Payments
Protecting transaction integrity, wallet security, and DPDP / RBI compliance for high-growth FinTech ecosystems.

E-commerce & Digital
Proving transaction integrity and privacy controls to consumer protection bodies.
Powered by the QuassrCyberTech ecosystem
Platform intelligence that accelerates delivery, strengthens execution, and improves measurable outcomes.

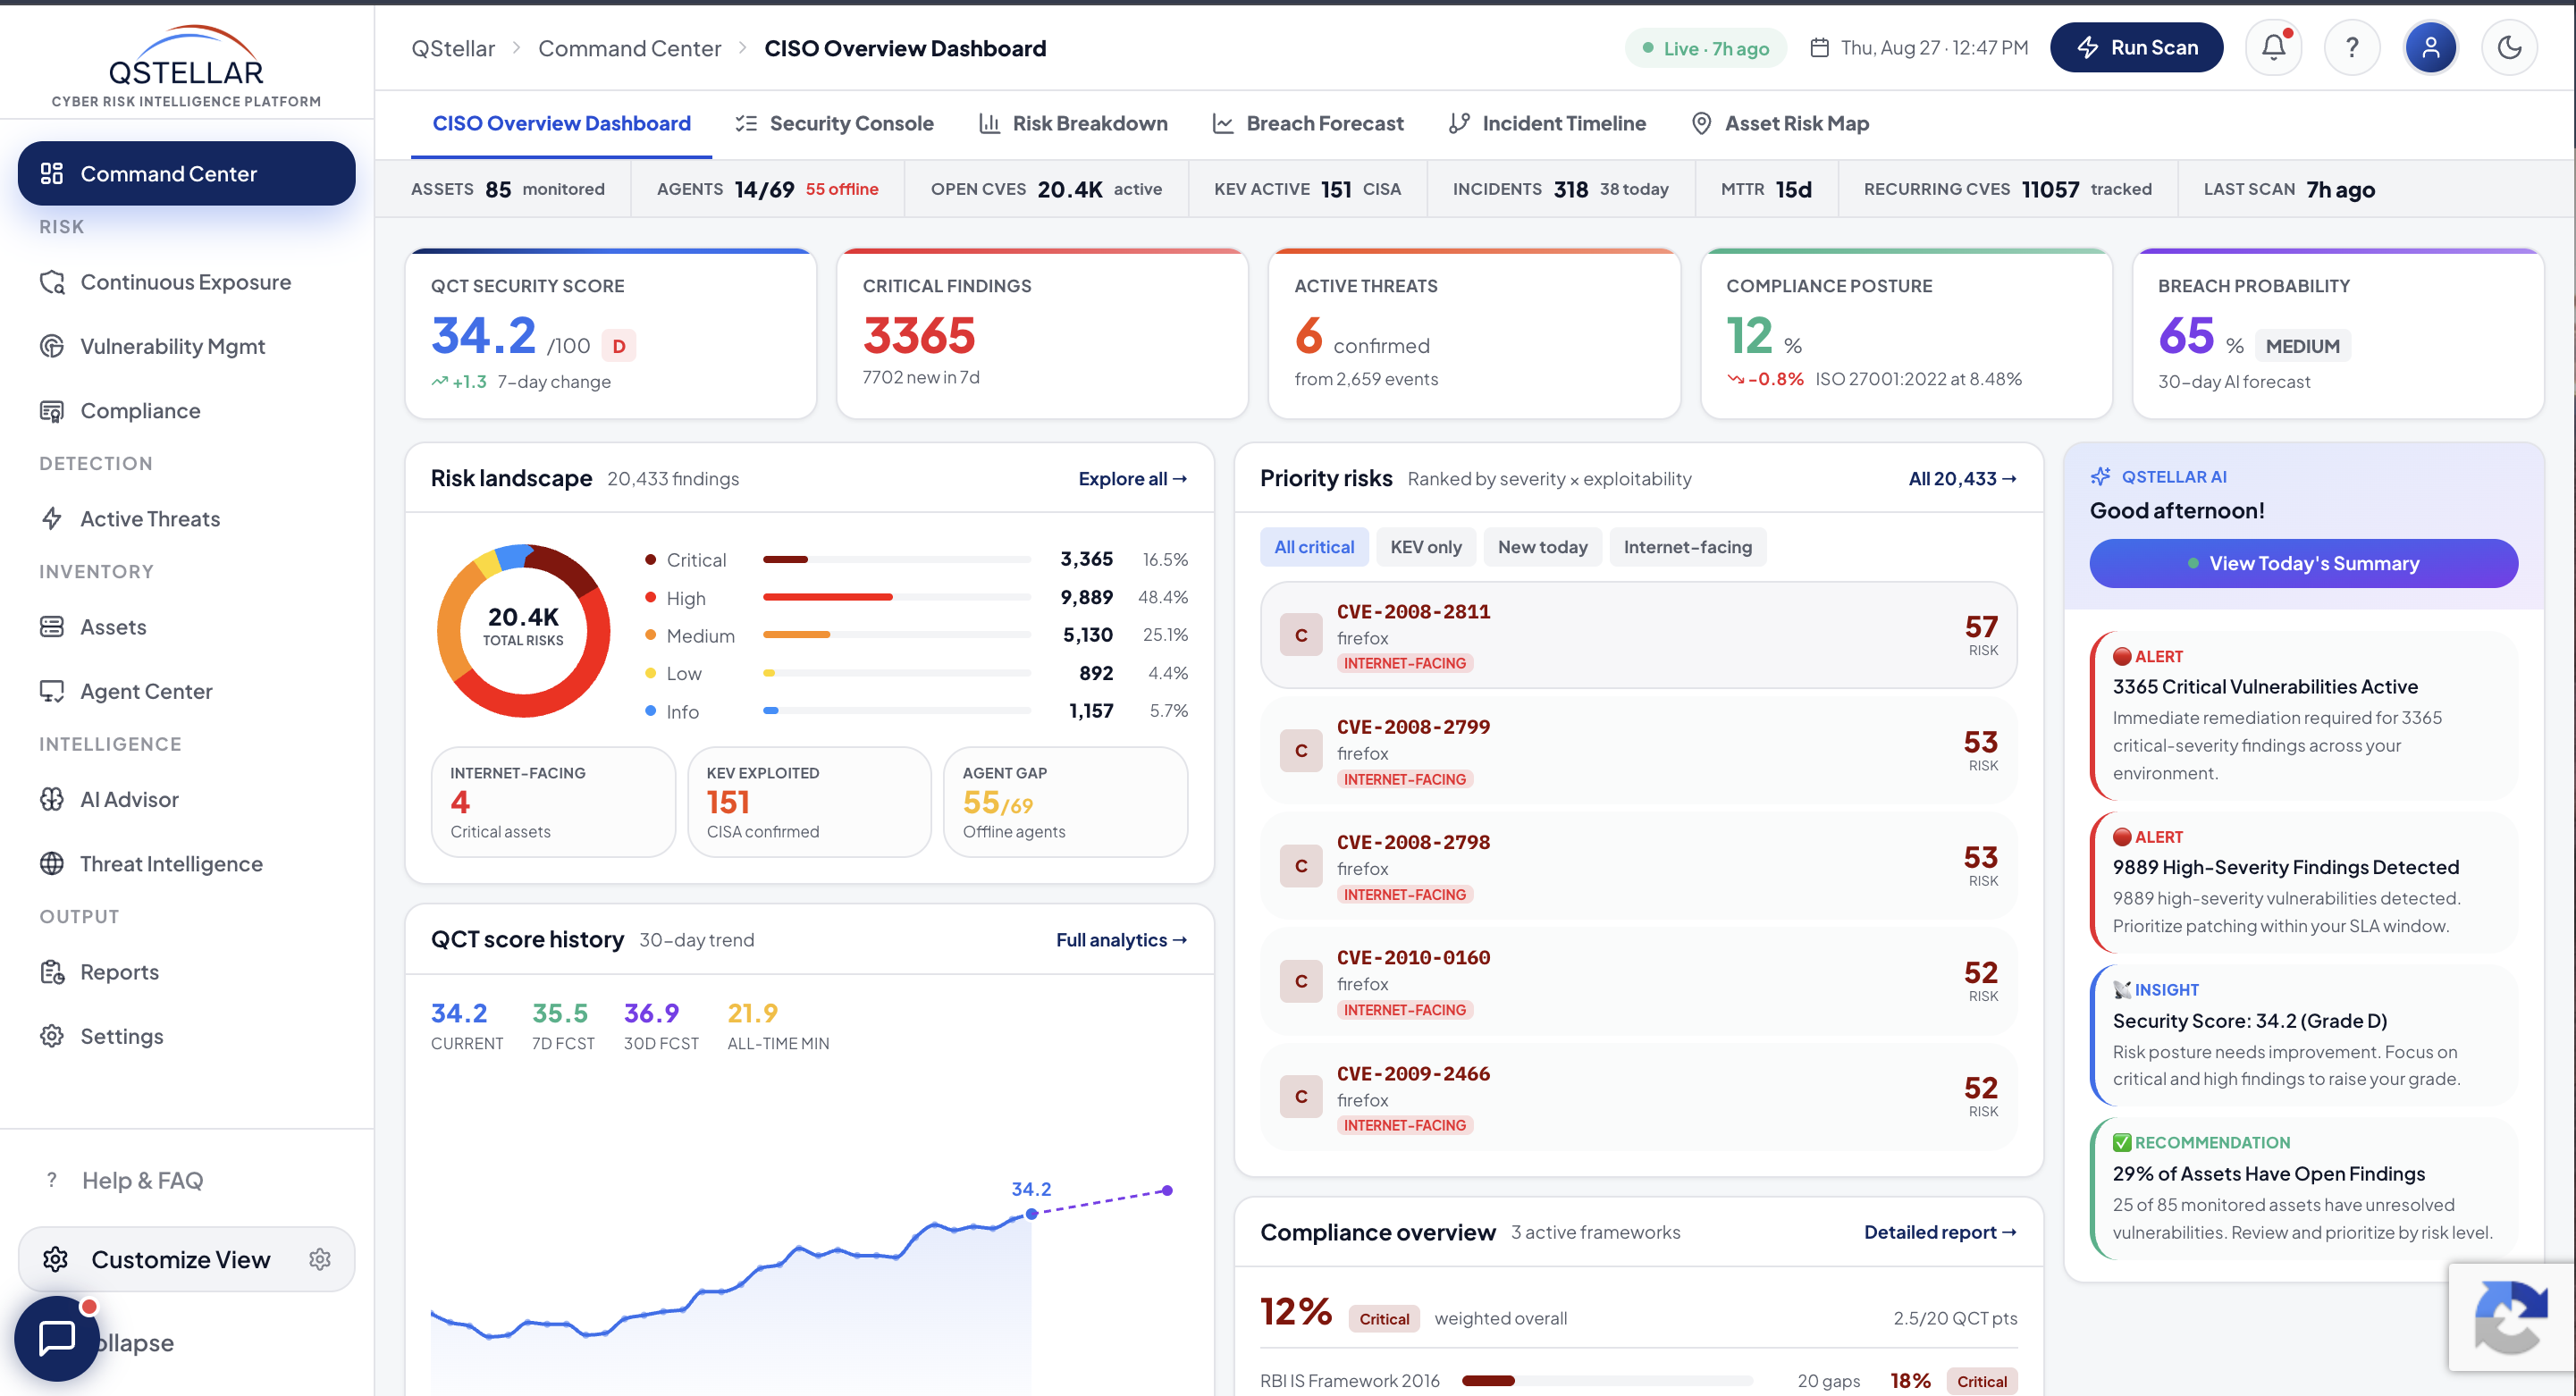
AI-Powered Asset Intelligence & Vulnerability Management
Our SOC2 Readiness engagements are accelerated by QStellar, combining platform intelligence with advisory and execution delivery.
- Asset discovery and continuous visibility
- Vulnerability intelligence with risk prioritization
- Configuration drift and exposure monitoring
Frequently Asked Questions
Answers to common questions for SOC2 Readiness.
Related Capabilities
Explore adjacent capability pillars commonly delivered alongside this engagement stream.
READY TO BEGIN?
Secure Your Digital Enterprise
Partner with QuassrCyberTech to strengthen cyber resilience, governance, and security operations.