A gap assessment compares your current security controls against the specific requirements of a target regulation or industry framework. It provides a clear, documented view of where your organization currently stands and identifies the exact areas where you fall short of compliance. This serves as the foundational step for any compliance journey or security improvement project.

Regulatory Gap Assessment
Know where you stand before regulators do. Our gap assessments give you a clear, honest picture of compliance posture and a prioritized remediation roadmap.

Scope of Assessment
What We Assess
The areas we examine during a Regulatory Gap Assessment engagement, and what each one is looking for.
01
Control Mapping
Map current operational controls against specific, applicable regulatory requirements.
02
Policy Completeness
Analyze documentation, standard operating procedures, and policies for audit readiness.
03
Evidence Verification
Verify and gather technical implementation evidence for compliance controls.
04
Vendor Compliance
Evaluate vendor and supply chain compliance posture and exposure risk.
05
Audit History
Assess previously identified audit findings, open items, and remediation progress.
Also in Scope
Regulatory applicability mapping across all applicable jurisdictions and industry verticals
Control ownership and accountability assignment across business functions
Gap prioritization methodology based on risk severity and regulatory penalty exposure
Data classification alignment with regulatory data handling and retention requirements
Cross-regulation overlap analysis to identify shared and conflicting control obligations
Emerging regulatory developments and their anticipated impact on current compliance posture
Security awareness and training requirements mandated by applicable regulations
Breach notification obligations and incident reporting timelines per regulatory framework
Contractual compliance obligations flowing from regulatory requirements to third parties
Remediation roadmap development with milestone-based closure tracking
Engagement Sequence
How QuassrCyberTech Delivers
A structured delivery sequence that converts assessment insights into measurable resilience outcomes.
01
Scoping
Define applicable regulations, frameworks, and assessment boundaries.
02
Assessment
Conduct control-by-control gap analysis and technical evidence review.
03
Reporting
Deliver a comprehensive gap report featuring risk-rated findings.
04
Roadmap
Provide a clear remediation plan with assigned ownership and timelines.
Where This Lands
Industry Application
Banking & Financial Services
Identifying compliance gaps across RBI mandates before formal audits occur.
FinTech & Digital Payments
Assessing readiness for complex multi-framework financial regulations.

Healthcare & HealthTech
Evaluating data protection controls against stringent health privacy laws.
Powered by the QuassrCyberTech ecosystem
Platform intelligence that accelerates delivery, strengthens execution, and improves measurable outcomes.

AI-Powered Asset Intelligence & Vulnerability Management
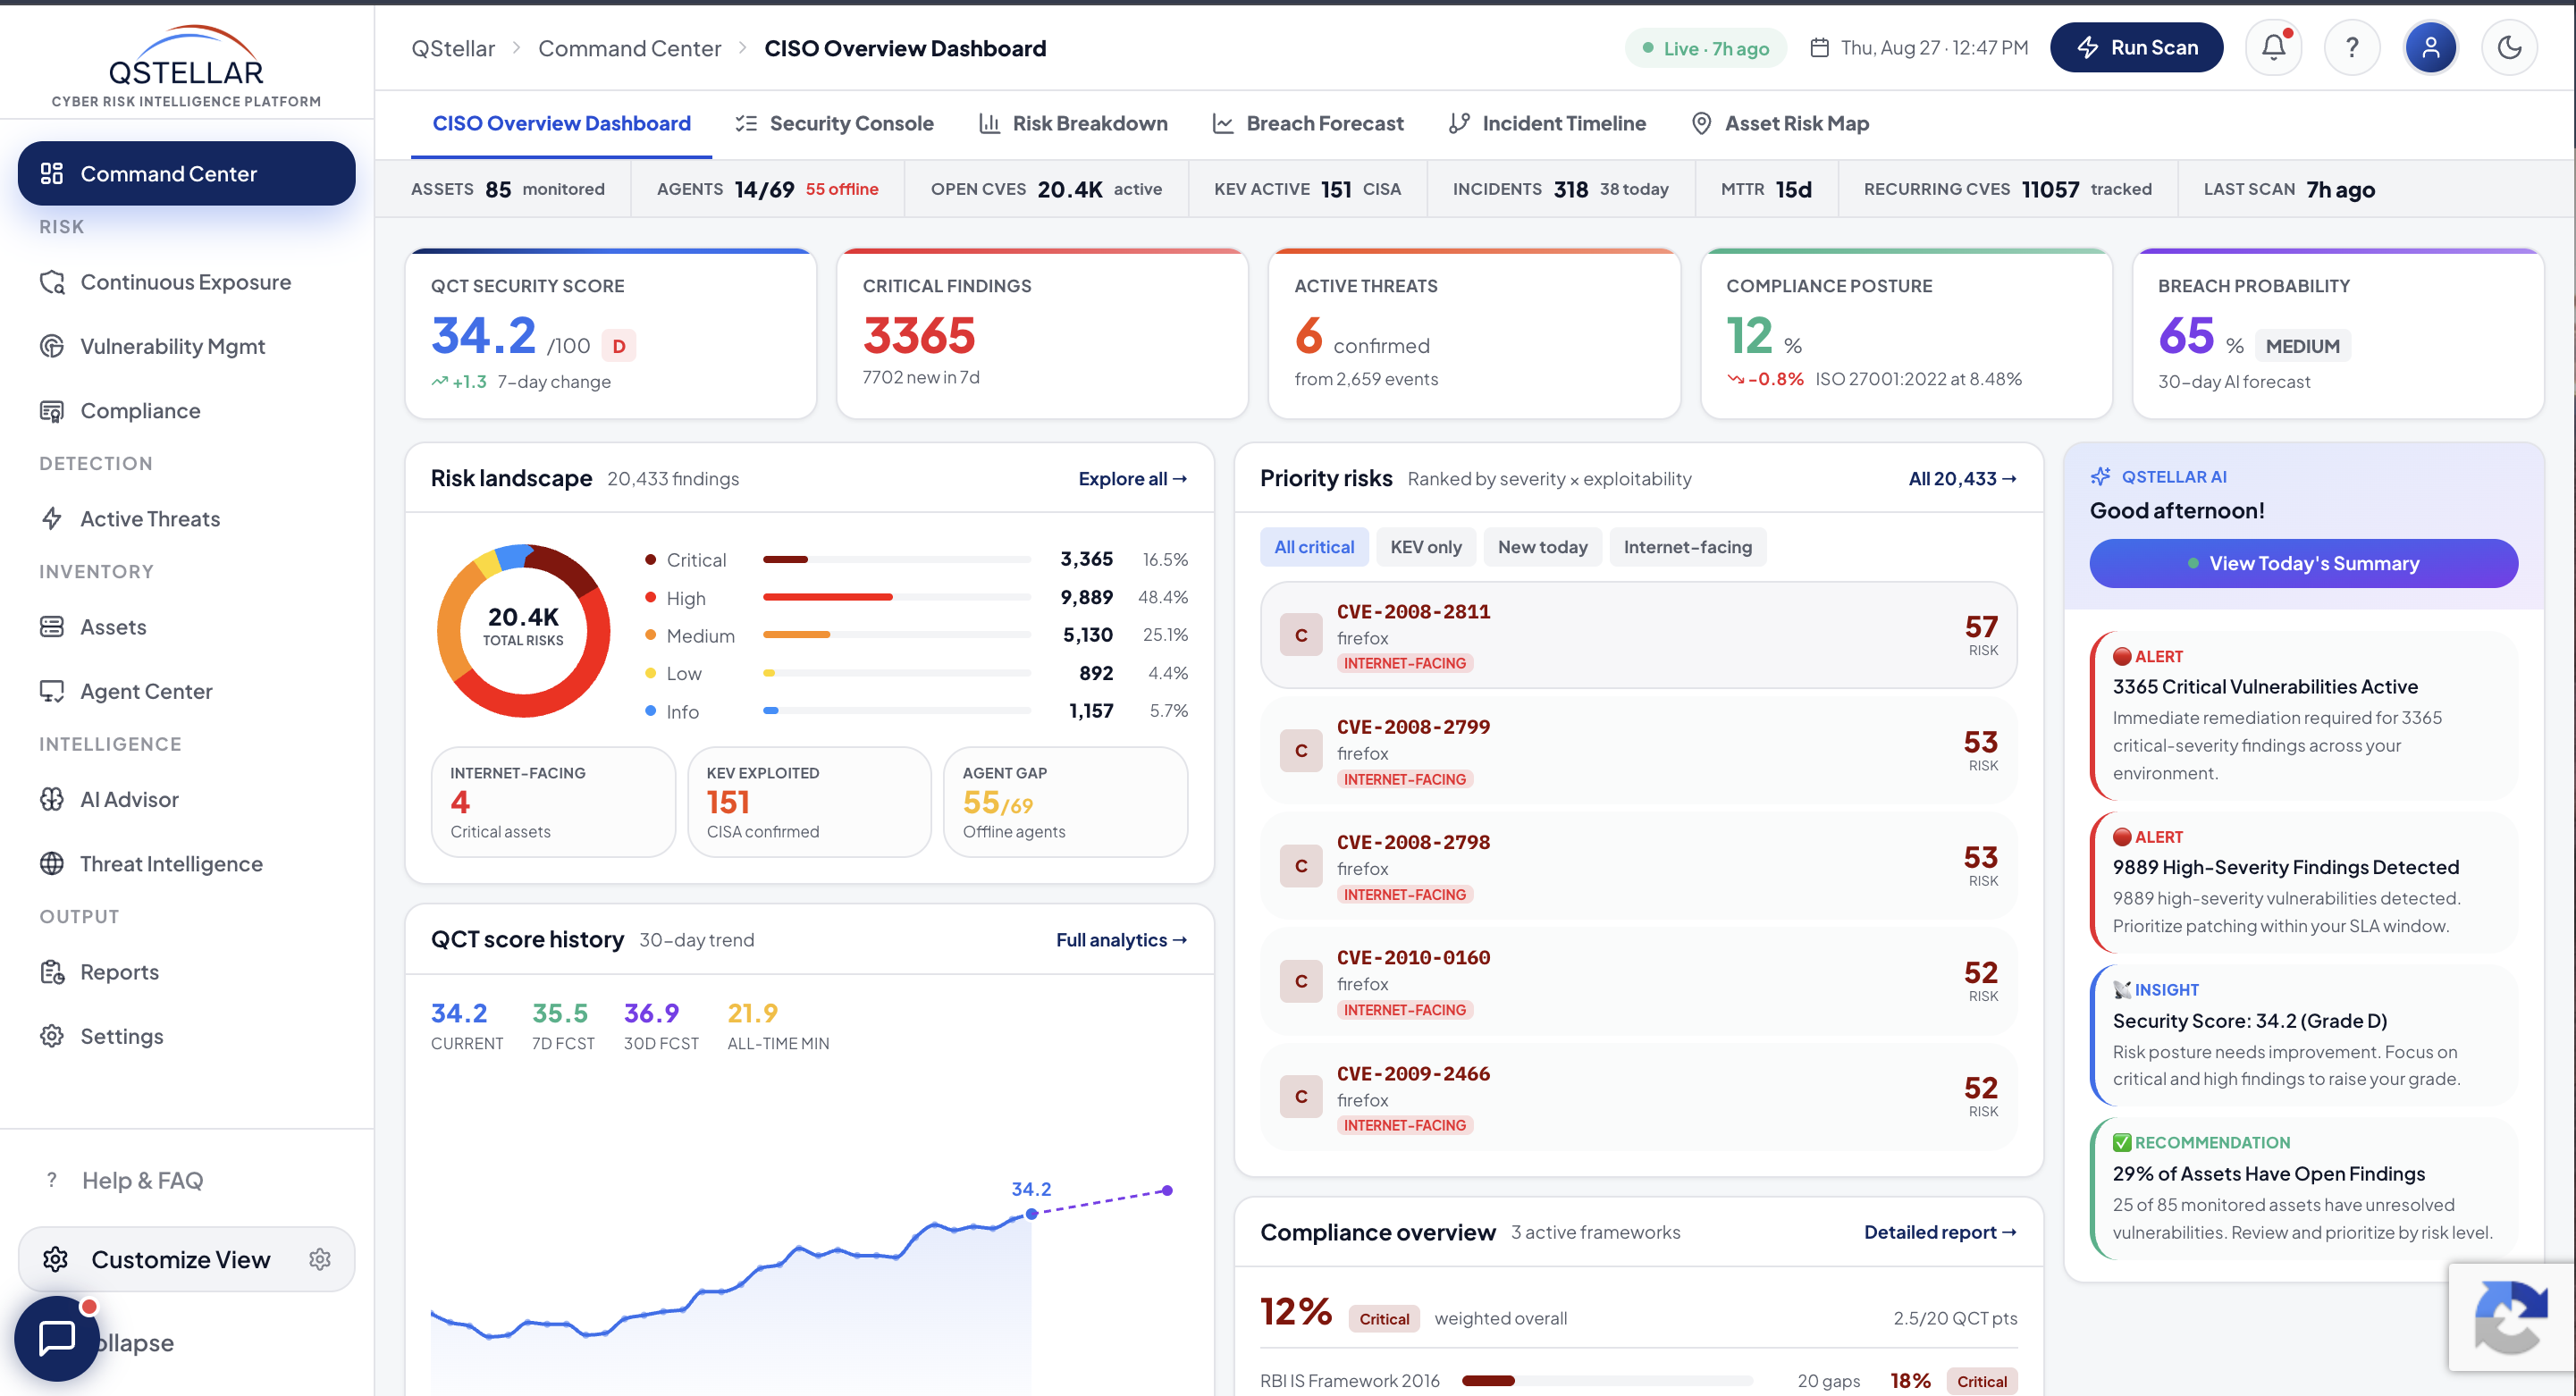
Our Regulatory Gap Assessment engagements are accelerated by QStellar, combining platform intelligence with advisory and execution delivery.
- Asset discovery and continuous visibility
- Vulnerability intelligence with risk prioritization
- Configuration drift and exposure monitoring
Frequently Asked Questions
Answers to common questions for Regulatory Gap Assessment.
Related Capabilities
Explore adjacent capability pillars commonly delivered alongside this engagement stream.
READY TO BEGIN?
Secure Your Digital Enterprise
Partner with QuassrCyberTech to strengthen cyber resilience, governance, and security operations.