
A pentest is designed to find as many vulnerabilities as possible in a specific scope, whereas a Red Team engagement is a stealthy, goal-oriented adversary simulation. It tests your organization's real-world detection and response capabilities by emulating the behavior of a persistent threat. While a pentest checks the locks, a Red Team engagement tries to get to the vault undetected.

Red Teaming
A red team engagement simulates a sophisticated, goal-oriented attacker targeting your organization - testing your defenses across technical and human dimensions.
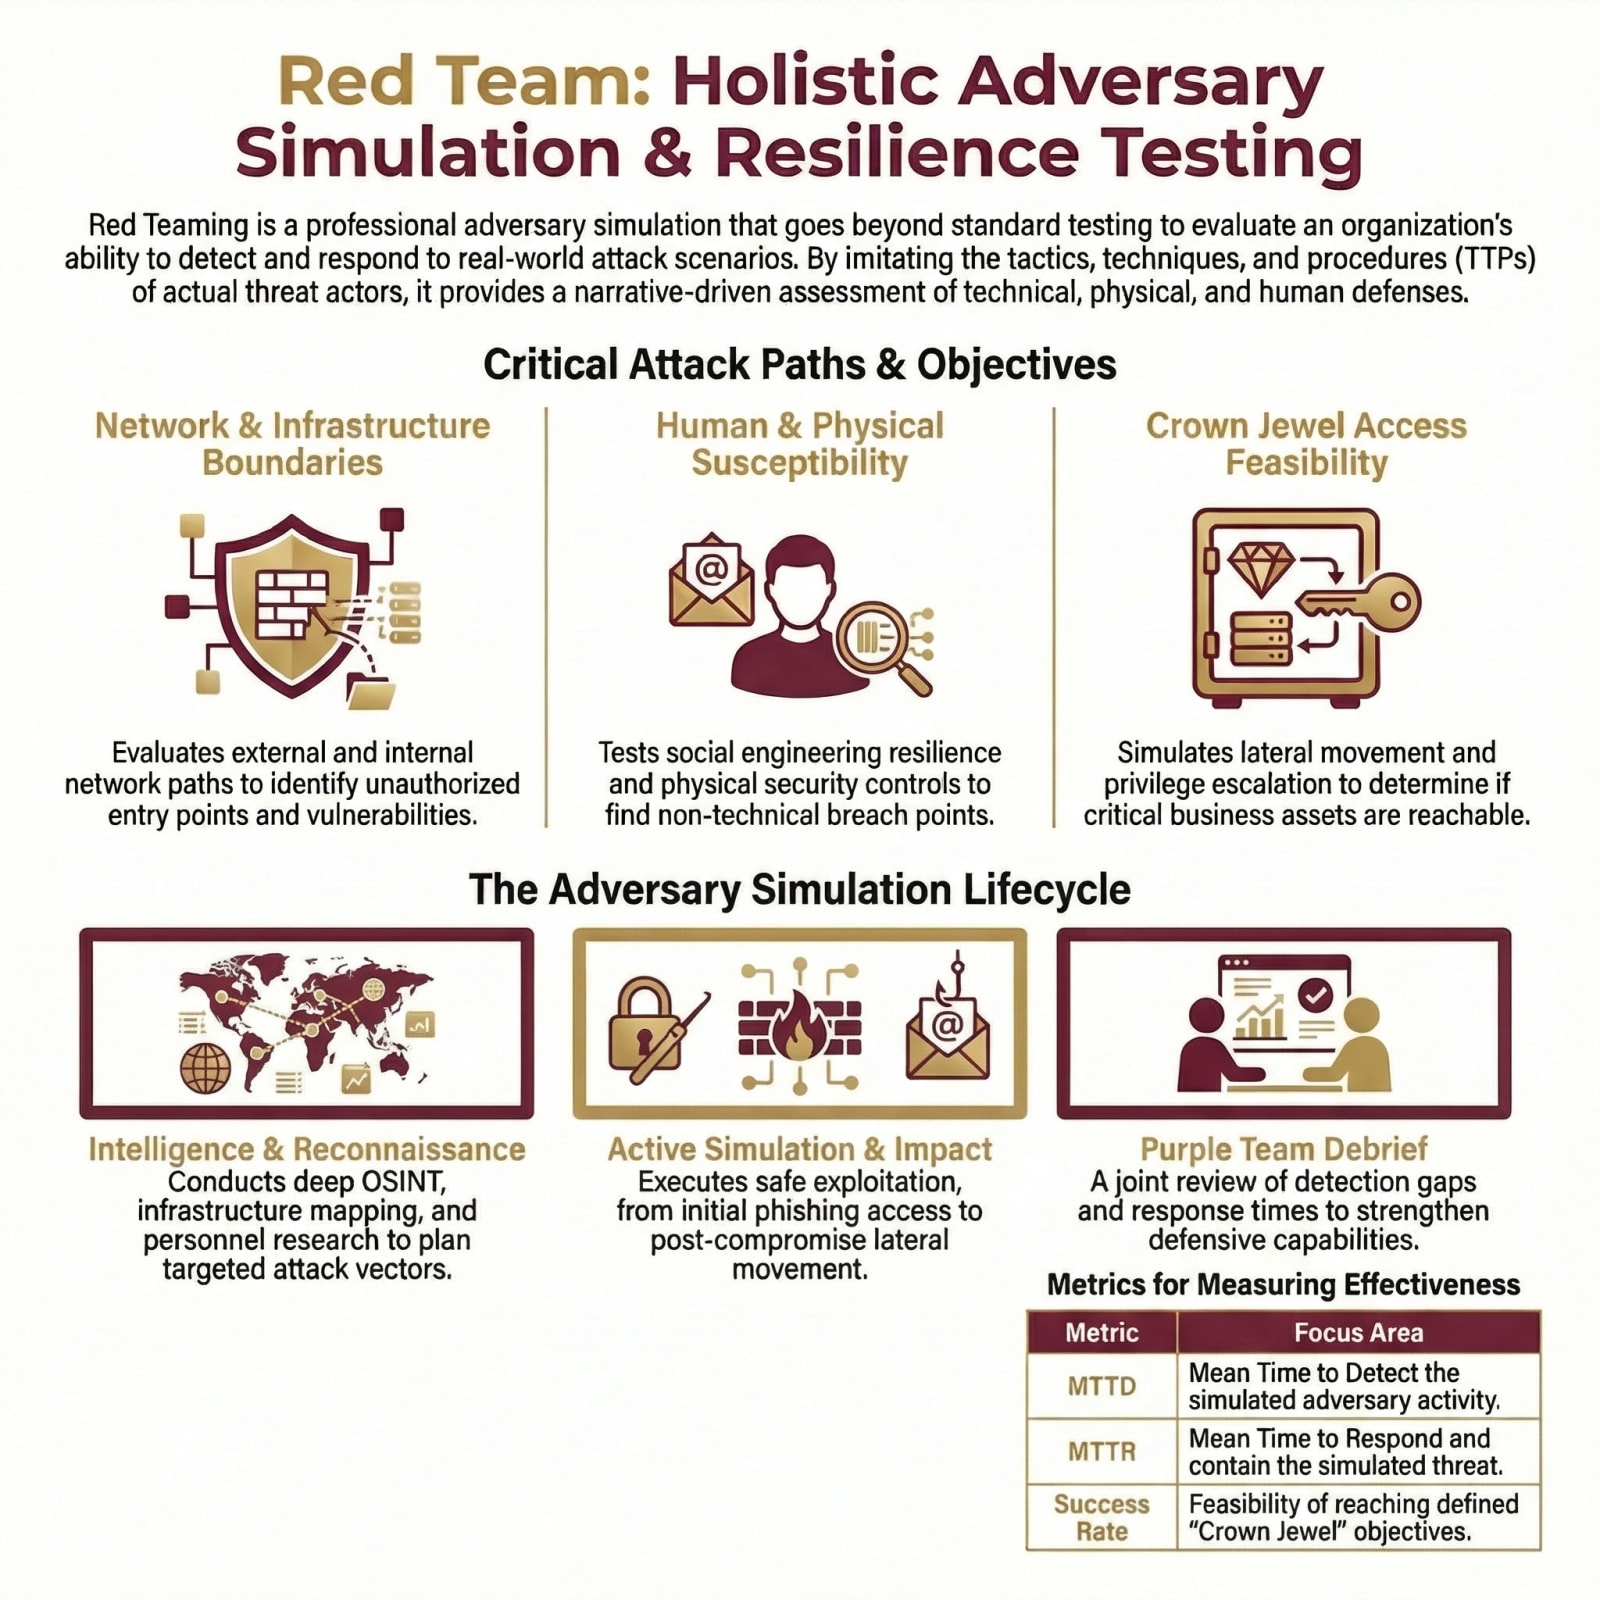
Scope of Assessment
What We Assess
The areas we examine during a Red Teaming engagement, and what each one is looking for.
01
Network Attack Paths
Expose reachable external services and exploit internal lateral network paths.
02
Physical Security
Assess physical access controls, surveillance systems, and badge entry points.
03
Social Engineering
Measure employee susceptibility to phishing, vishing, and tailgating tactics.
04
Incident Detection Efficacy
Test internal security team detection speed and incident response accuracy.
05
Lateral Threat Movement
Simulate lateral movement methods and exploit Active Directory permissions.
06
Crown Jewel Security
Evaluate technical feasibility of compromising critical servers or databases.
Also in Scope
Data exfiltration feasibility and egress control bypass assessment
Cloud environment attack surface exploitation and misconfiguration abuse
Supply chain and third-party access vector exploitation scenarios
Persistence mechanisms and long-term foothold establishment techniques
Domain trust abuse and Active Directory attack path exploitation
Email and collaboration platform compromise and account takeover feasibility
Wireless and network perimeter attack surface evaluation
Insider threat simulation and abuse of legitimate user privileges
Application-layer attack paths leading to critical system compromise
Post-exploitation impact assessment against business-critical data and services
Engagement Sequence
How QuassrCyberTech Delivers
A structured delivery sequence that converts assessment insights into measurable resilience outcomes.
01
Threat Profiling
Identify the most relevant threat actors and map their TTPs using MITRE ATT&CK.
02
Reconnaissance
Conduct OSINT, map external infrastructure, and research personnel.
03
Simulation
Execute simulated attacks, from initial phishing access to post-exploitation lateral movement.
04
Purple Team Debrief
Jointly review detection gaps and defensive responses with your internal team.
Where This Lands
Industry Application
Banking & Financial Services
Testing the holistic resilience of financial institutions against targeted, advanced persistent threats.
Enterprise & Manufacturing
Simulating aggressive ransomware actors to test SOC detection and operational resilience.

Healthcare & HealthTech
Evaluating physical and digital security controls protecting highly sensitive medical networks.
Powered by the QuassrCyberTech ecosystem
Platform intelligence that accelerates delivery, strengthens execution, and improves measurable outcomes.

Penetration Testing as a Service Platform
Our Red Teaming engagements are accelerated by QRGT, combining platform intelligence with advisory and execution delivery.
- Continuous penetration testing workflow
- Centralized findings and remediation tracking
- Governed collaboration across red-blue teams
Frequently Asked Questions
Answers to common questions for Red Teaming.
Related Capabilities
Explore adjacent capability pillars commonly delivered alongside this engagement stream.
READY TO BEGIN?
Secure Your Digital Enterprise
Partner with QuassrCyberTech to strengthen cyber resilience, governance, and security operations.