Kubernetes is a highly complex and dynamic orchestrator, and a single misconfiguration can expose the entire cluster to compromise. We provide specialized hardening to secure both the Kubernetes control plane and the individual workloads running within it. Our approach ensures that your containerized environment is resilient, manageable, and secure at scale.

Kubernetes & Container Security
Kubernetes security is a distinct discipline. Misconfigurations in clusters, images, and runtime can expose entire environments. We assess the full container lifecycle.

Scope of Assessment
What We Assess
The areas we examine during a Kubernetes & Container Security engagement, and what each one is looking for.
01
Kubernetes RBAC
Audit Kubernetes role-based access control policies and service account permissions.
02
Pod Security Control
Evaluate Pod Security Standards (PSS) and admission controllers usage.
03
K8s Network Policies
Audit network policy enforcement to isolate namespaces and restrict inter-pod traffic.
04
Container Hardening
Scan container base images and verify security configurations inside files.
05
Kubernetes Secrets
Review secrets storage encryption, external vault integrations, and injection paths.
06
Control Plane Security
Verify API server authentication and check database (etcd) encryption keys.
Also in Scope
Runtime container behavior monitoring and anomaly detection coverage
Container registry security, image signing and supply chain integrity controls
Node hardening and underlying host operating system security configuration
Namespace isolation effectiveness and workload separation enforcement
Persistent volume and storage security within containerized environments
Cluster upgrade cadence, version currency and known CVE exposure assessment
Engagement Sequence
How QuassrCyberTech Delivers
A structured delivery sequence that converts assessment insights into measurable resilience outcomes.
01
Cluster Audit
Perform automated and manual assessments of the Kubernetes control plane and API server.
02
Configuration Review
Analyze RBAC, network policies, and admission controllers for least privilege.
03
Image Scanning
Identify vulnerabilities and misconfigurations within container images.
04
Reporting
Provide cluster-level and workload-level remediation strategies.
Where This Lands
Industry Application

SaaS & Technology
Securing massive, microservices-based architectures running on managed or self-hosted Kubernetes.
FinTech & Digital Payments
Isolating highly sensitive financial workloads within containerized environments.

E-commerce & Digital
Securing customer data, payment processing, and mobile commerce applications for digital retail leaders.
Powered by the QuassrCyberTech ecosystem
Platform intelligence that accelerates delivery, strengthens execution, and improves measurable outcomes.

AI-Powered Asset Intelligence & Vulnerability Management
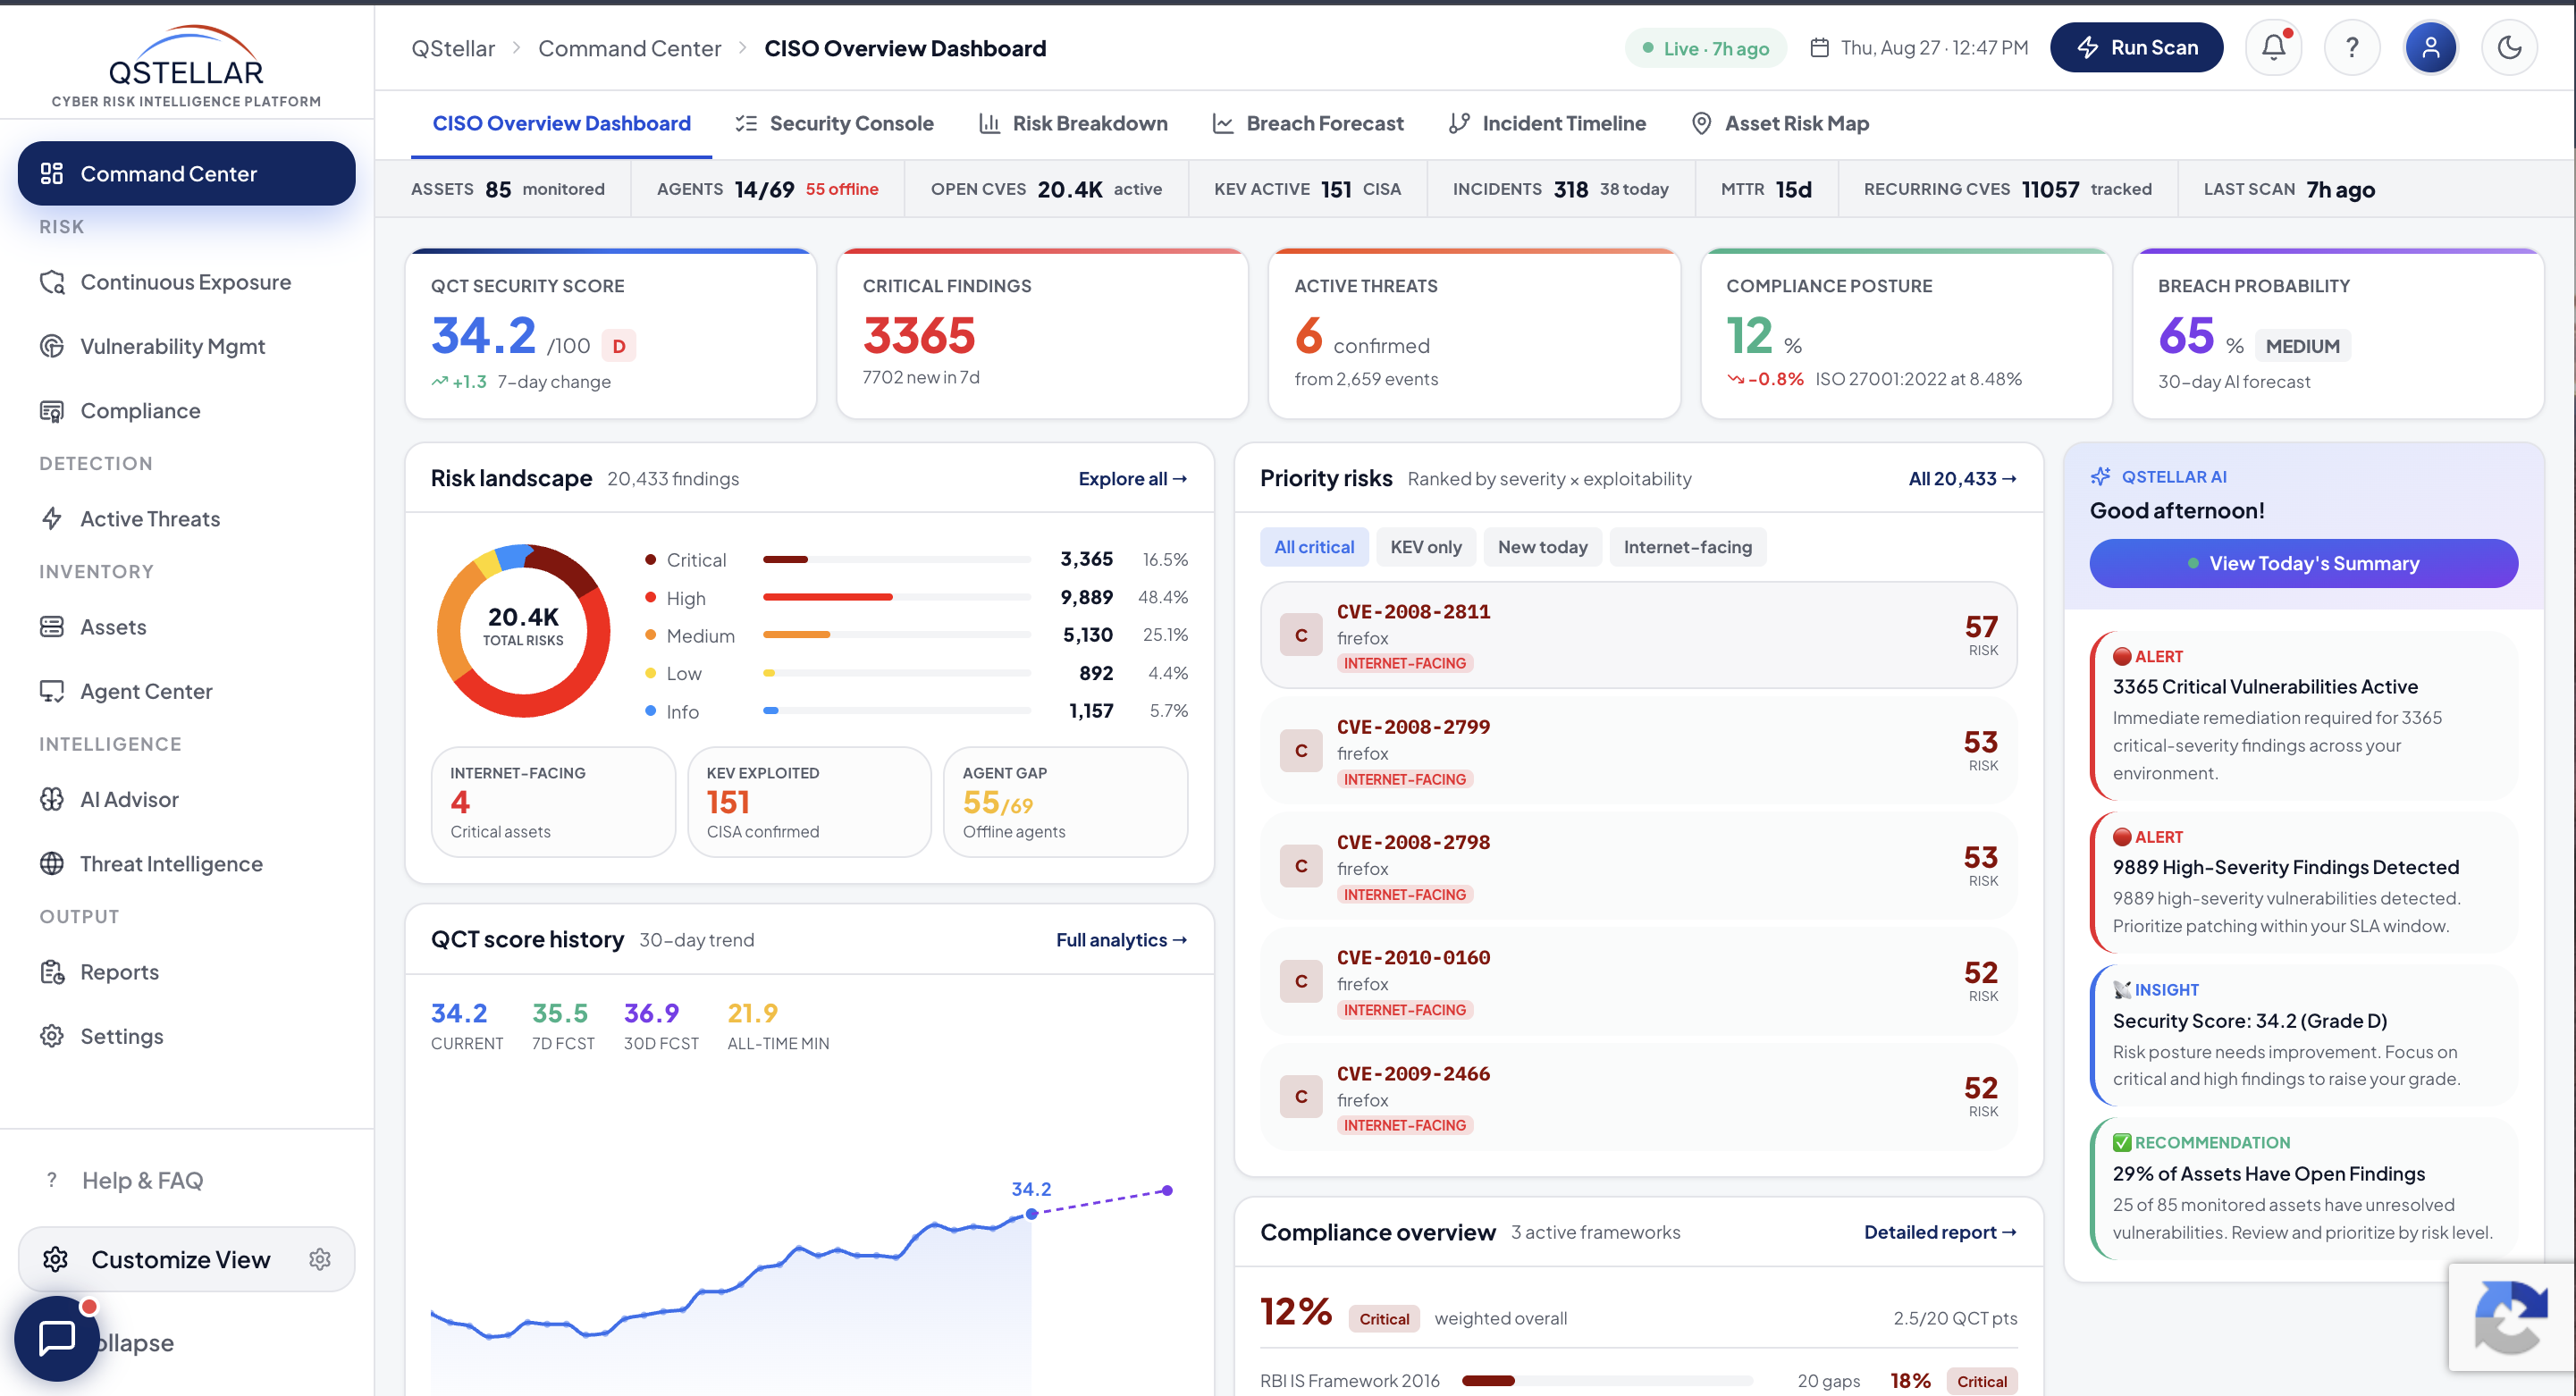
Our Kubernetes & Container Security engagements are accelerated by QStellar, combining platform intelligence with advisory and execution delivery.
- Asset discovery and continuous visibility
- Vulnerability intelligence with risk prioritization
- Configuration drift and exposure monitoring
Frequently Asked Questions
Answers to common questions for Kubernetes & Container Security.
Related Capabilities
Explore adjacent capability pillars commonly delivered alongside this engagement stream.
READY TO BEGIN?
Secure Your Digital Enterprise
Partner with QuassrCyberTech to strengthen cyber resilience, governance, and security operations.